 RePerspective Labs
INSIGHT
Deep Dive
Controls by Design: Making AI Implementation Governable from Day One
Build controls that can be demonstrated, sustained, and revalidated as the operation changes.
Executive summary
An AI-enabled workflow can produce useful results while its controls remain unproven. Permission limits may exist only in instructions, monitoring may miss the relevant failure, and exceptions may reach people without a workable response. Controls by design makes governability part of what the operation must demonstrate before launch. Each critical control needs an implementation point, evidence that it works, and an owner responsible for its continued effectiveness. The leadership decision is to fund and accept that operating capability alongside the business functionality. As policies, knowledge, and system components change, the evidence must be renewed. A successful launch is the beginning of that responsibility.
The question
What proves that the controls will work in everyday operations?
A deployment review can establish that an AI capability answers questions, prepares recommendations, or completes a workflow. It can also confirm that the required policies and approvals exist. Those findings leave another question open: will the intended controls actually govern the work?
Consider the difference between a policy requiring current information and a workflow that checks which policy version supports a response. Or between naming an escalation owner and demonstrating that a case reaches that person with enough context to resolve it.
These are implementation questions with business consequences. A missed control can expose customers to incorrect decisions; an unnecessarily restrictive one can delay service and consume scarce attention. Leaders need evidence that the chosen controls protect the intended outcome under the conditions in which the operation will run.
My perspective
I would treat a critical control as unfinished until the team can demonstrate where it acts, what evidence it produces, and how the operation responds when it fails. That changes what leaders accept as delivery. The business inherits a capability it can inspect, challenge, and maintain, with clear responsibility for keeping the controls effective as the work changes.
Shashi Sethi
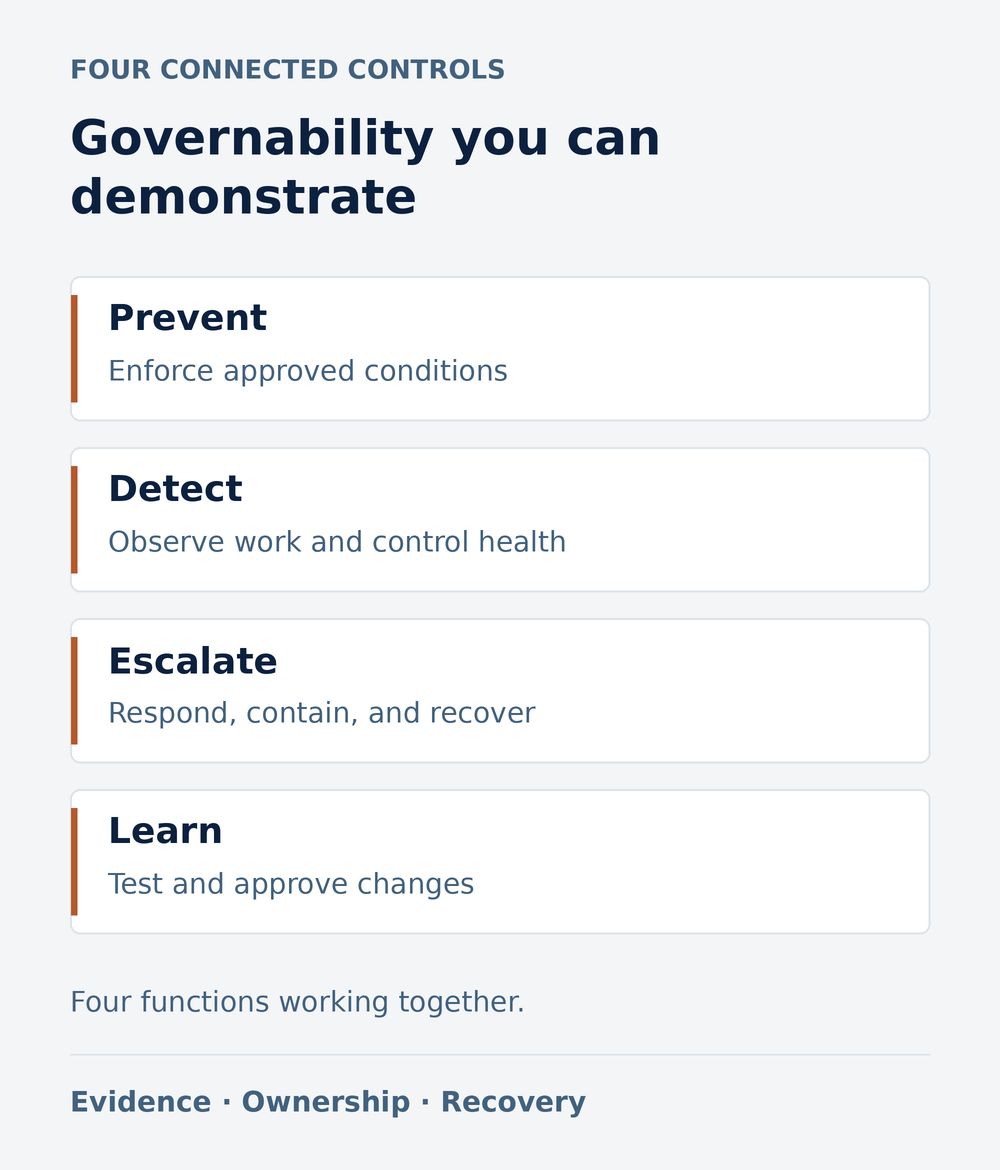
Prevent, Detect, Escalate, and Learn work together to make controls enforceable, observable, actionable, and adaptable. Evidence and named ownership connect all four.
The approach
Turn governance intent into an operating requirement
Start with the business outcome the control must protect. In a service operation, that might be a timely, correct answer that preserves the customer’s entitlements and privacy. Faster response generation is useful only within that wider purpose.
The Bounded Autonomy Insight addresses which decisions and actions the enterprise should delegate. Controls by design takes those agreed limits into implementation: where they are enforced, how failure is recognized, and what evidence the business can inspect.
For each material risk, describe the expected behavior at the point where it matters. “Use approved knowledge” becomes a requirement to identify the applicable source, check its approval and effective version, and hold the affected action when that cannot be established. Specify who owns the source and who resolves the held case.
Then make the requirement testable. Identify a condition that should activate the control, the expected response, and the record that would demonstrate it happened. A control described in a design document has a different status from one implemented, exercised, and observed in operation.
In the Transformation Operating Map, this article’s main home is Deploy into Operations. The control requirements must enter design and build early enough to be demonstrated before that transition.
Connect Prevent, Detect, Escalate, and Learn
The existing RePerspective Labs vocabulary remains useful. These are connected functions that may operate at different moments, rather than four steps every case must follow. Prevention can route a case directly to a person; detection may uncover an error after an action; learning should improve all the controls.
Prevent: enforce the conditions for action
Put enforceable restrictions in the workflow and the systems that execute actions. A capability limited to reading customer records should receive the corresponding access. A requirement for human approval should be checked before the consequential action can proceed.
OWASP’s 2026 Excessive Agency guidance recommends limiting tool functionality and permissions and implementing authorization checks outside the model’s own judgment. The implementation test is whether an unauthorized action is blocked even when the model proposes it.
Knowledge needs equivalent treatment. Approved sources, effective dates, access rights, and applicability should travel with the work. A recent document is not necessarily the governing document. Where interpretation remains ambiguous, the control should route that ambiguity to a qualified person.
These measures constrain what can happen. They do not establish that every permitted answer or action is correct.
Detect: observe both the work and the controls
Monitor whether the operation produces acceptable outcomes and whether the control mechanisms themselves are functioning. A quiet alert queue is inconclusive if the alerting process has stopped working.
For policy-dependent responses, sample completed work against the applicable source, including cases that raised no exception. NIST’s Generative AI Profile, published July 2024, recommends checking generated sources and citations during evaluation before deployment and continuing that verification during operation. A citation’s presence alone should not count as proof of a supported answer.
Retain enough evidence to reconstruct consequential events: the relevant input, source and system versions, control result, action taken, and human intervention. Design access and retention around the sensitivity of that evidence; logging everything indefinitely is not a sensible default.
Use this record to examine missed exceptions, unnecessary holds, recurring errors, and gaps in control coverage. A persuasive explanation generated by the model should not substitute for a record of what the workflow actually did.
Escalate: connect the signal to a response and recovery
An alert needs an operational destination: a responsible person, sufficient evidence, an expected response time, and authority to intervene. Test the receiving workflow as well as the alert. Staff need time and practice to investigate, challenge, and resolve cases; a queue cannot create that capacity by itself.
Define the response when an essential control becomes unavailable. Depending on the work, that could mean holding affected actions, routing them to a staffed alternative, or reducing automated intake. Preserve service continuity without treating an unanswered escalation as approval.
Also distinguish stopping further activity from repairing its consequences. If an incorrect response has already reached a customer, disabling the system leaves the earlier advice unresolved. The operation needs a way to identify affected cases and coordinate correction.
NIST’s AI Risk Management Framework 1.0, January 2023, connects mechanisms for disengaging unsuitable systems with post-deployment incident response, recovery, and change management. Those capabilities belong in the implementation scope.
Learn: make corrections part of controlled change
An override or incident should produce a decision about what needs to change. The cause may be an outdated source, a poorly placed control, an unrealistic escalation rule, or a problem in the underlying service process.
Assign an owner to that change, test the affected behavior, and retain the evidence supporting release. Recheck that the correction has not weakened another control. Keep a workable fallback while the change is evaluated.
Learning here means improving how the operation works. It does not require a model to retrain itself during live service. A better source-approval process or a clearer exception route may be the most useful improvement.
Follow one policy change through the operation
Hypothetical operating example — a proposed design, not a reported deployment or measured result.
A service team wants to reduce the time employees spend finding policy information and preparing routine customer responses. The proposed AI-enabled workflow retrieves the relevant policy, prepares a response, and sends it to an employee for approval. Existing authority over customer commitments remains with that employee.
Now change a policy. The risk is that a draft based on the former version remains in the approval queue, looks plausible, and is sent after the new policy takes effect. Human approval alone has not resolved the knowledge problem.
The implementation should be able to demonstrate the following behavior:
| Control point | Required operating behavior | Evidence to inspect |
|---|---|---|
| A replacement policy becomes effective | The knowledge owner approves the applicable version. Affected pending drafts are flagged for revalidation before release. | Source approval and version record; identification of affected drafts; revalidation results. |
| A draft lacks a valid policy reference | The release path holds the response and sends the case, with its missing evidence, to the designated reviewer. | Held action, receiving team, and recorded resolution. |
| A required version check is unavailable | Release of affected drafts stops. Cases move to manual verification against the authoritative policy, with support and Operating owners notified. | Control-health alert, completed manual verification, and disposition of queued work. |
| An outdated answer has already been sent | The Operating owner identifies affected cases, arranges appropriate corrections, and verifies the fix before normal processing resumes. | Affected-case record, corrective action, and results of the repeated control test. |
Illustrative acceptance evidence for one policy-dependent workflow. The controls would need to be adapted to the service’s actual obligations, systems, and risks.
Test valid cases too. If an unaffected response is repeatedly held, the control may be protecting the wrong scope or relying on an unreliable signal. The acceptance evidence should cover both the intended intervention and the work that should proceed.
The proposed benefit is faster preparation with fewer preventable policy errors and less correction work. Validate it against the existing service baseline, including employee review time, incorrect responses, rework, queue age, and the cost of maintaining the controls. The example establishes a way to test that proposition; it does not establish a realized benefit.
Keep the evidence valid after go-live
Control evidence describes a particular configuration operating under particular conditions. A change to the policy source, retrieval method, prompt, model, permissions, or downstream workflow can affect what was demonstrated. The scope of retesting should follow the dependencies affected by the change.
Keep the approved configuration identifiable, and connect material changes to the relevant control tests. When a supplier changes a component, determine whether the change affects the operation’s acceptance evidence. A supplier’s assessment can inform that review, but it cannot describe every consequence of the enterprise’s own workflow configuration.
Reuse established access management, monitoring, incident handling, and change processes where they fit. Extend them where AI introduces a different failure mode. Each workflow still needs evidence that those shared controls operate correctly in its context.
This is also a funding decision. Knowledge maintenance, quality sampling, reviewer capability, support, and retesting continue after implementation. The operating owner should know which responsibilities and costs the business is accepting.
Proportion matters. Control depth should reflect the consequences of failure and the scope of the work. Measure missed failures and unnecessary intervention alongside service performance. Additional controls can add delay and cost; their value must be judged through the outcomes they protect and the operating burden they create.
Leadership takeaway
Ask for evidence from the control itself
At the next implementation review, choose one critical control and ask the team to demonstrate it in a safe test environment. Introduce the condition it is meant to catch. Inspect the resulting action, the evidence recorded, and the response from the people who would operate it. Then remove a dependency that the control relies on and repeat the exercise.
Before accepting delivery, ask the operating owner to explain which future changes would invalidate that evidence and who is responsible for repeating the test. Include the resources required to keep that commitment.
The result is a more concrete acceptance decision: which controls have been demonstrated, which remain uncertain, and what scope can responsibly enter service. Day-one governability begins with evidence the business can continue to produce.
Sources and further reading
Evidence used in this article
- NIST — Artificial Intelligence Risk Management Framework (AI RMF 1.0), January 2023. MANAGE 2.4 and MANAGE 4.1 address disengagement, monitoring, incident response, recovery, and change management. Voluntary guidance supporting the operating practices discussed here.
- NIST — Artificial Intelligence Risk Management Framework: Generative Artificial Intelligence Profile (NIST AI 600-1), July 2024. MS-2.5-003 recommends verifying sources and citations during evaluation and ongoing monitoring.
- OWASP GenAI Security Project — LLM03:2026 Excessive Agency, 2026 edition. Supports limited permissions and authorization enforcement outside the model’s judgment. Official project repository; accessed 12 September 2026. The inspected file does not display a publication day.
The acceptance approach and hypothetical example are RePerspective Labs’ proposed application of these principles. These sources support specific practices; they do not establish the article’s proposed business benefits as measured outcomes.